
Granola should not be used for patient consultations, telehealth visits, clinical handoffs, or other conversations containing protected health information (PHI). Its current security FAQs say it is not HIPAA compliant and cannot sign a Business Associate Agreement (BAA).
For a doctor evaluating documentation tools, that limitation comes before transcription quality or convenience. Granola is a general meeting note-taker, not a verified medical scribe, EHR integration, or clinical decision-support system.
What Granola actually does
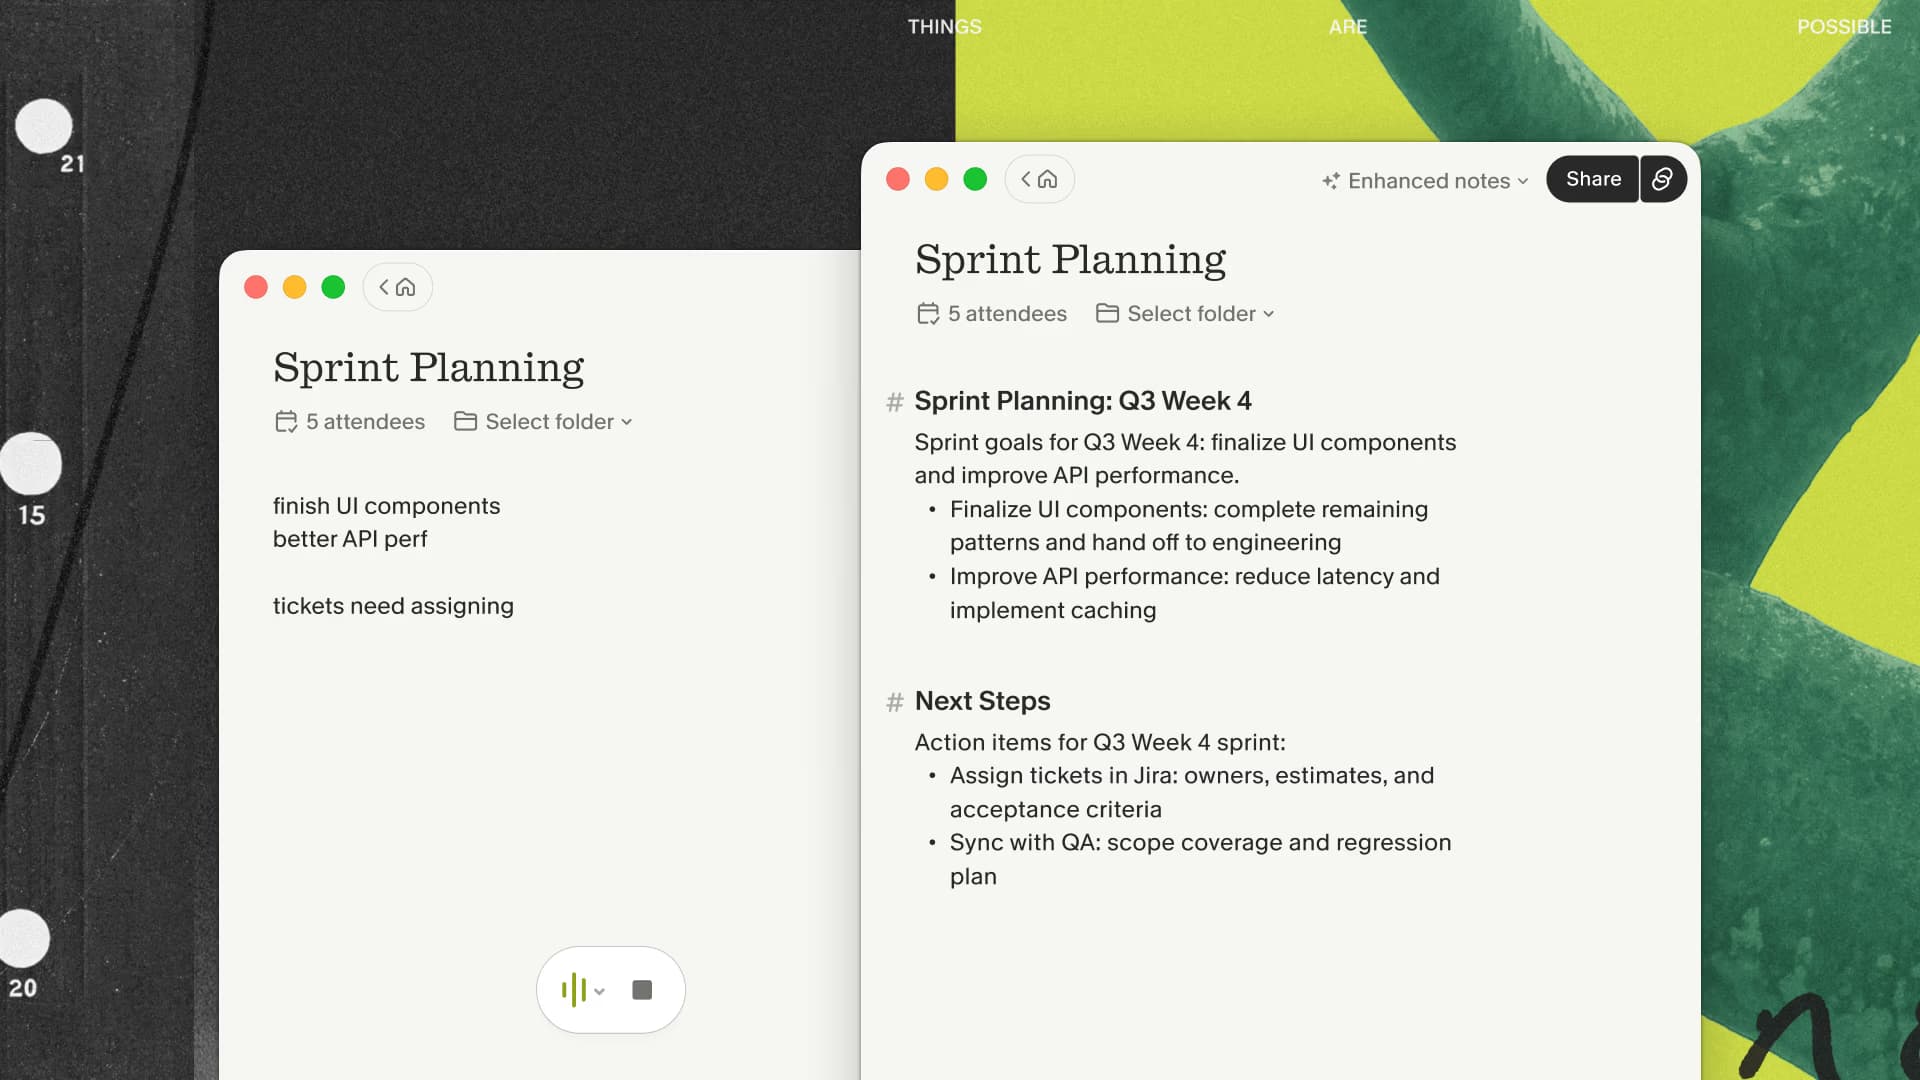
The transcription documentation describes a desktop app for macOS and Windows that captures microphone and system audio without a meeting bot. It passes audio to a transcription provider; Granola says it does not record or save audio or video. Cloud AI processing produces enhanced notes from meeting context and your typed notes.
Bot-free capture is not local-only processing. Granola's security FAQs describe US AWS storage, encryption in transit and at rest, and retention of notes and transcripts unless a retention policy is configured. A local note cache does not keep the conversation off cloud services.
Keep patient information out of the workflow
Do not use Granola to transcribe or summarize:
- Patient visits, including remote consultations
- Rounds, discharge planning, or case conferences containing PHI
- Medication changes, diagnoses, lab results, or insurance details tied to patients
- Dictation intended for a patient chart
- Administrative meetings where patient information is likely to come up
Patient consent alone does not resolve the missing BAA or make this a HIPAA-compliant service. Removing names after transcription is also too late to prevent the original information from being processed. Ask your privacy team what qualifies as properly de-identified information; do not assume that omitting a name is enough.
The medical transcription guide explains the vendor and workflow requirements to check for clinical use.
A narrow non-clinical evaluation
A practice could consider Granola for an explicitly approved meeting category that excludes PHI, such as planning public website content or discussing office equipment. Even those conversations need a clear boundary: a routine operations meeting can turn into a discussion of an identifiable patient.
Before any evaluation:
- Have the privacy or compliance owner approve the exact meeting category.
- Explain cloud transcription to participants and obtain the consent required by law and policy.
- Set retention, sharing, and model-training preferences before capture.
- Agree to stop transcription if the discussion crosses the approved boundary.
- Define who handles an accidental disclosure and how it is reported.
If that boundary cannot hold during a normal conversation, use manual notes or a different approved tool. For a stable non-clinical category only, evaluate Granola on a low-risk administrative meeting.
What to require for clinical documentation
For patient-facing work, evaluate a medical documentation vendor against your practice's requirements. Request a BAA covering the intended service, documented PHI handling, access controls, audit evidence, retention and deletion terms, and a supported health-record workflow.
Test accuracy with your specialty's terminology and establish clinician review before anything enters the chart. A fluent summary can omit a negation, confuse medication quantities, or turn a tentative assessment into a diagnosis. Do not infer clinical accuracy from a general meeting demo.
The official sources cited here do not establish direct EHR imports, billing-code suggestions, clinical decision support, or compliance with Joint Commission, CMS, or specialty documentation standards for Granola. Those are capabilities to verify with a clinical vendor, not promises to attach to this product.
Recommendation
Use an approved clinical documentation system for patient encounters. Consider Granola only for a separately approved, non-clinical meeting set with no PHI. The enterprise security review covers the cloud storage, sharing, and retention questions that still apply outside clinical work.
Recheck Granola's security FAQs and current contract before changing that boundary. A future announcement would still require verification of the BAA, plan coverage, and your organization's approval.
Discussion
Giscus